
AI speed, human judgment
Managed Detection & Response that stops threats before they disrupt your business
Attackers now use AI, automation and stolen credentials to move faster than most businesses can respond. TTG MDR delivers always-on detection with human-led response, 24/7.
Under attack or locked out by ransomware? Call our incident response line now: (713) 824-1035
Why Modern MDR Matters
Most security tools generate alerts. Few actually stop the attack.
Today’s threats:
- Move across endpoints, cloud, identity, and apps
- Use automation and AI to evade detection
- Exploit gaps between tools and response teams
MDR closes that gap.
With TTG MDR, threats are:
- Detected in real time
- Investigated automatically or by analysts
- Contained immediately—without delay
What is Managed Detection & Response (MDR)?
Managed Detection & Response (MDR) is a fully managed cybersecurity service that combines three core capabilities into one always-on defense.
Advanced Detection Tools
EDR/XDR, SIEM, and identity monitoring, unified into one detection layer.
24/7 SOC Coverage
Continuous coverage from a staffed Security Operations Center (SOC).
AI + Human Response
AI-driven analysis with human-led investigation and response.
Unlike traditional security solutions, MDR doesn’t just alert—it acts.
The TTG MDR Advantage
AI Handles Speed. Humans Own the Outcome.
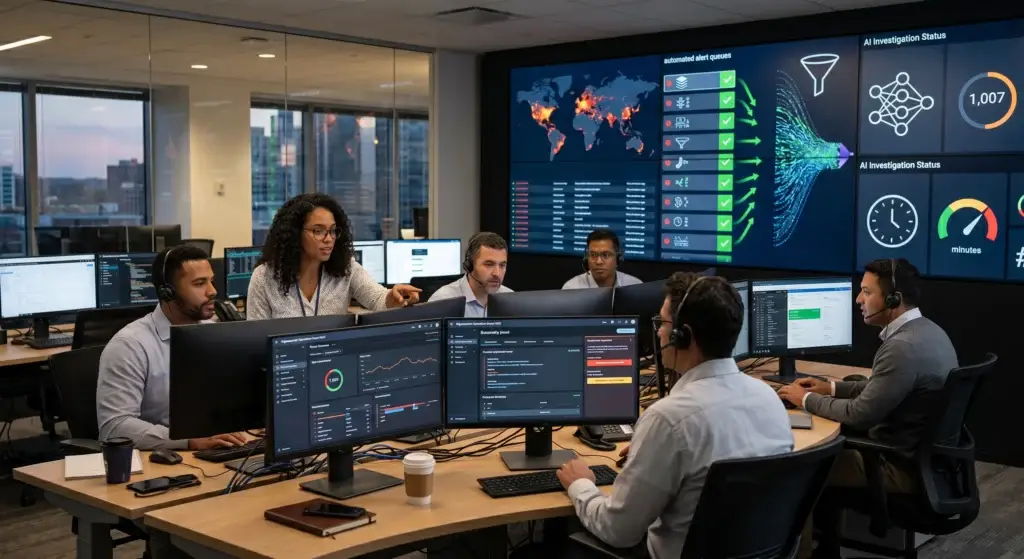
We combine automation and expertise to deliver faster and smarter protection:
AI investigates alerts in seconds
Automation reduces noise and false positives
Human analysts validate, decide, and respond
The result: faster containment, fewer disruptions, and full accountability.
Advanced Detection Across Your Entire Environment
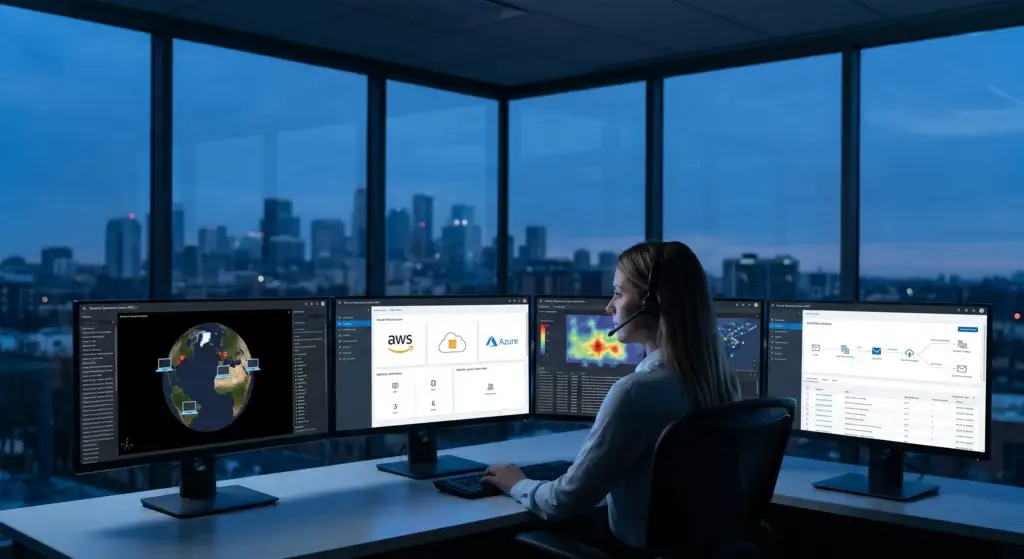
Track threat activity across:
- Endpoints (laptops, servers, devices)
- Cloud platforms and SaaS applications
- User identities and access systems
- Email and collaboration tools
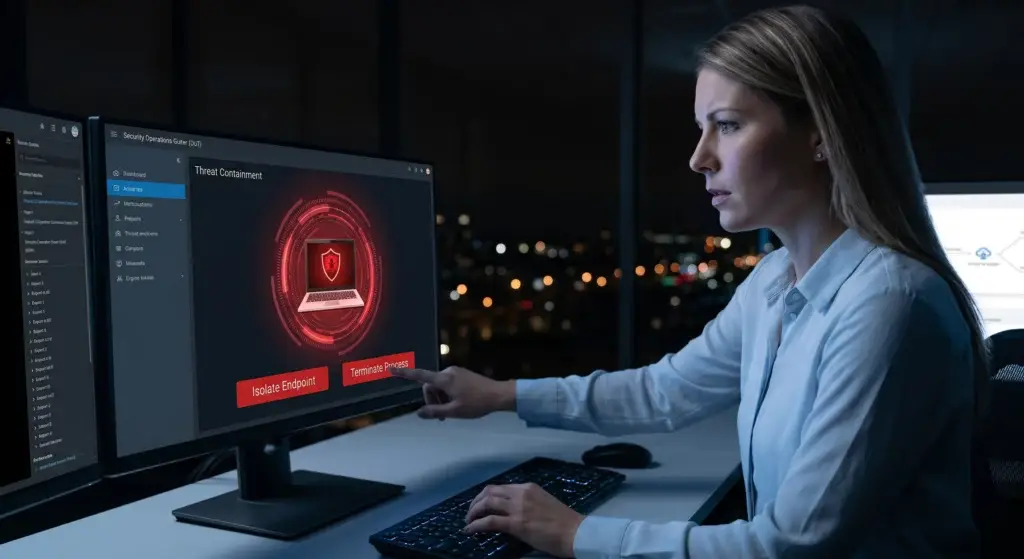
Real-Time Threat Containment
When threats are confirmed, we act immediately:
- Isolate compromised devices
- Terminate malicious processes
- Block attacker access
- Protect credentials and user accounts
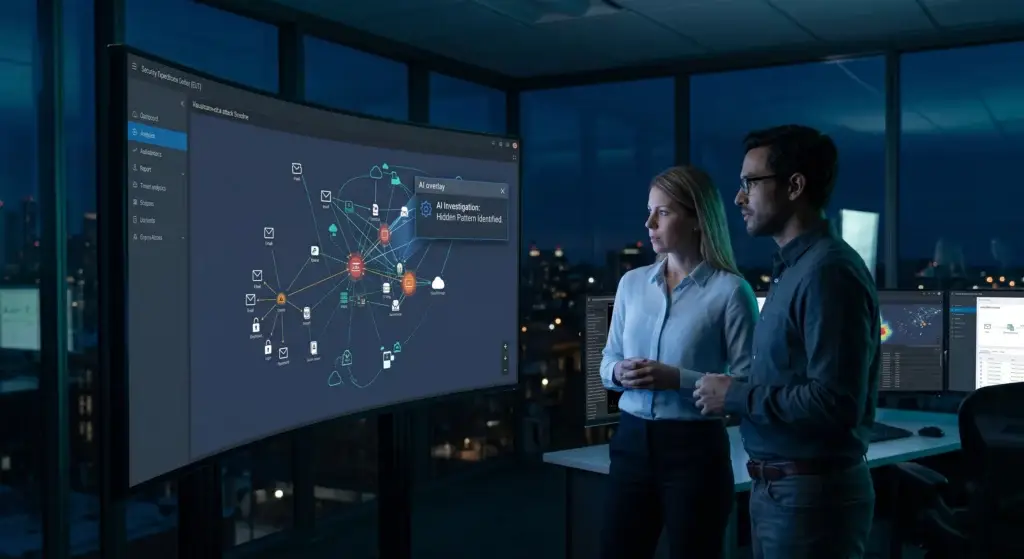
AI-Accelerated Threat Investigation
Automation and AI:
- Analyze alerts at scale
- Correlate activity across systems
- Identify hidden attack patterns
- Reduce response time dramatically
Proactive Threat Hunting
We don’t wait for alerts—we actively search for threats:
- Behavior-based investigations
- Intelligence-driven threat analysis
- Detection of stealth and advanced attacks

Vendor-Agnostic Integration
Bring your existing tools—or use ours. We integrate with:
- Microsoft security solutions
- Endpoint protection platforms
- Cloud and identity providers
- SIEM and logging systems

Scalable Protection Across Your Business
Secure:
- Remote and hybrid employees
- Cloud environments
- On-prem infrastructure
- Business applications and data
Our Approach: Detect. Respond. Improve.
1. Detect: Identify threats early with real-time visibility across your entire environment.
2. Respond: Contain and stop attacks immediately using automated and human-led responses.
3. Recover: Guide remediation, investigate root causes, and restore operations quickly.
4. Improve: Continuously strengthen your defenses using threat intelligence and detection tuning.
Built for the Modern Threat Landscape
Attackers are Moving Faster
AI-driven phishing, credential theft, and automated attacks are accelerating risk.
Your Attack Surface is Expanding
Data flows across email, cloud apps, collaboration tools, and remote devices.
Defense Requires More Than Tools
Effective protection requires:
Continuous monitoring
Deep expertise
Immediate response capability
That’s exactly what MDR delivers.
Need Managed IT or Co-Managed IT Support for your business?